By Adetunji Oludele Adebayo, CISM
Artificial intelligence is becoming borderless, but the rules governing it are not. A technology company can develop one AI solution for customers across multiple continents, yet face different compliance expectations in every market it enters. For established technology companies, this creates additional regulatory responsibilities. For smaller businesses, it raises a more difficult question: can they afford to compete in a global market where demonstrating compliance may require resources comparable to those needed to develop the technology itself?
As a Lead Information Security Consultant and GenAI Governance, Risk and Compliance specialist, I consider regulatory fragmentation one of the defining challenges facing emerging AI companies. My experience across cybersecurity governance, ISO 27001, NIST frameworks and financial-sector compliance has shaped a fundamental view: effective regulation should be measured by the risks it controls, not the amount of documentation it demands.
The European Union’s AI Act provides a comprehensive risk-based framework, with several provisions applicable since August 2026 and further high-risk requirements scheduled for 2027 and 2028. The United Kingdom relies substantially on existing sector regulators, while American states are establishing distinct obligations for automated decision-making.
These different approaches are understandable. Countries must protect their citizens according to their legal systems and economic priorities. Yet their combined effect can create disproportionate challenges for smaller technology businesses seeking international customers.
Consider a Nigerian startup developing an AI-powered credit assessment platform. Before offering its services internationally, it may need to demonstrate how the system handles personal information, assesses creditworthiness, prevents discriminatory outcomes and maintains appropriate human oversight.
The difficulty is not necessarily the existence of these requirements. It is that substantially similar controls may need to be assessed, documented and presented differently across jurisdictions.
My consultancy experience supporting a team responsible for PCI DSS recertification involving two Nigerian payment card processing organisations reinforces why this distinction matters.
In financial-sector cybersecurity, effective assurance requires more than written policies. Security controls must have clearly assigned owners, supporting evidence, documented testing and mechanisms for addressing weaknesses.
An organisation can maintain an impressive collection of compliance documents while still having poorly managed access privileges, inadequate monitoring or untested incident response procedures.
The same weakness can emerge in AI governance. A company might successfully complete multiple regulatory assessments without adequately demonstrating how its models respond to changing data, emerging risks or unexpected behaviour after deployment.
This is where I believe the international approach to AI compliance needs to evolve.
Rather than encouraging separate governance programmes for every market, regulators and standards bodies should work towards a common foundation for AI assurance evidence.
ISO/IEC 42001 and the NIST AI Risk Management Framework provide useful starting points. Both support structured approaches to identifying AI risks, assigning responsibilities and managing controls.
I would advocate a model in which technology companies maintain a central, independently assessable record of their AI systems, covering risk classification, data governance, security testing, model performance, human oversight and incident management.
That evidence could be mapped to the requirements of different jurisdictions, with additional assessments addressing specific local obligations.
This is not a proposal for universal regulatory approval. A system meeting one country’s requirements should not automatically qualify for deployment elsewhere. But where the underlying safeguards are equivalent, regulators should be able to recognise existing evidence instead of requiring companies to recreate it.
I also believe AI governance must move beyond compliance assessments conducted at isolated points in time.
Generative AI systems can change through model updates, new datasets and modifications to connected services. A risk assessment completed before deployment may no longer reflect the system’s behaviour months later.
Continuous control monitoring, documented model changes, periodic performance evaluations and clear escalation procedures should therefore become standard components of AI assurance.
These practices are familiar within information security governance. Applying them consistently to AI would strengthen accountability while giving smaller companies a more practical way to demonstrate responsible development.
There is also a responsibility on African regulators and industry leaders. As countries establish national AI governance approaches, they should consider how local businesses can meet international expectations without facing unnecessary duplication.
Shared regulatory guidance, accessible conformity assessment services and regional cooperation could make compliance more manageable without reducing consumer protection.
Some may argue that harmonising compliance evidence is unrealistic because regulatory priorities differ. I agree that complete legal uniformity is neither practical nor desirable. But harmonising the evidence used to demonstrate safeguards is different from harmonising the laws themselves.
That distinction is central to my argument.
The future of AI governance should not force regulators to choose between protecting the public and supporting smaller technology companies. Both objectives can be pursued through proportionate requirements, credible technical assurance and greater recognition of equivalent controls.
From my experience in cybersecurity and GenAI risk management, I believe the companies best prepared for this environment will be those that treat governance as an ongoing operational responsibility, not an exercise performed whenever an audit approaches.
Responsible AI should be judged by the effectiveness of its safeguards, not by the financial capacity of its developer to repeatedly prove the same controls.
If international regulators can move towards that standard, smaller technology companies will have a fairer opportunity to compete while the public benefits from stronger, more consistent assurance.
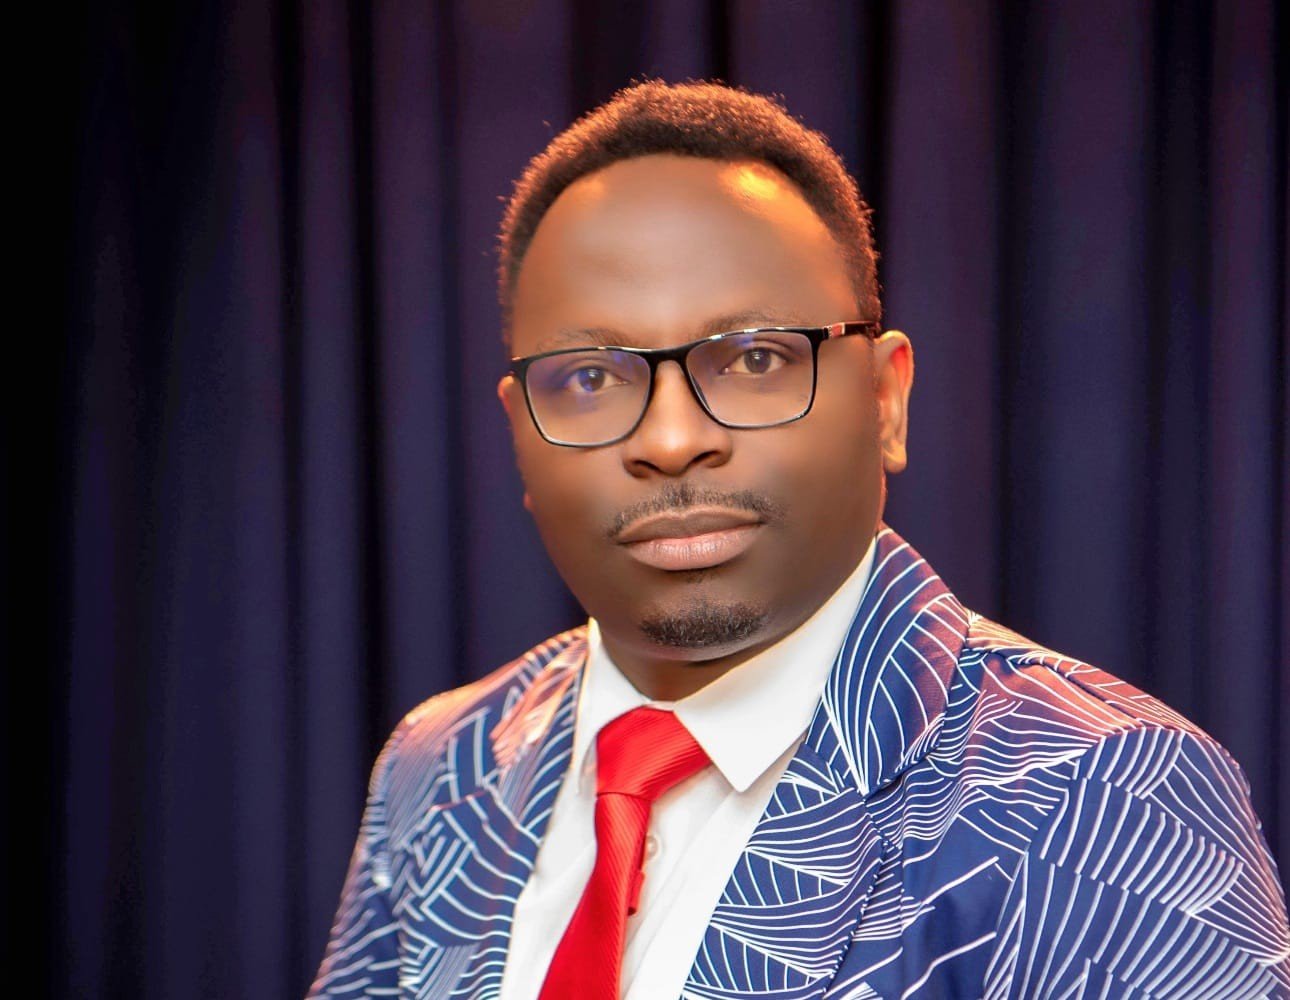
Adetunji Oludele Adebayo, CISM, is a Lead Information Security Consultant and GenAI Governance, Risk and Compliance specialist with over a decade of experience in cybersecurity and information security. A certified ISO/IEC 27001 Lead Implementer, his expertise includes NIST frameworks, PCI DSS, financial-sector security and operational risk management. He is an author, industry judge and recipient of the 2025 Global Recognition Award for Excellence in Cybersecurity and GenAI GRC.